Initial report
Needs attention
- Asset
- gateway.example
- Finding
- TLS configuration needs hardening
- Proposed action
- Update configuration and verify
- Condition
- Approval and maintenance window
NODO 1 (N1) · AUTONOMOUS SECURITY & COMPLIANCE OPERATOR
Nodo 1 (N1) brings IT support, cybersecurity and compliance into one operator. It detects risk, coordinates and executes authorized remediation, verifies the result and documents the evidence your organization needs to earn enterprise trust.
Trust is the outcome. Execution is the difference.
See plans and pricing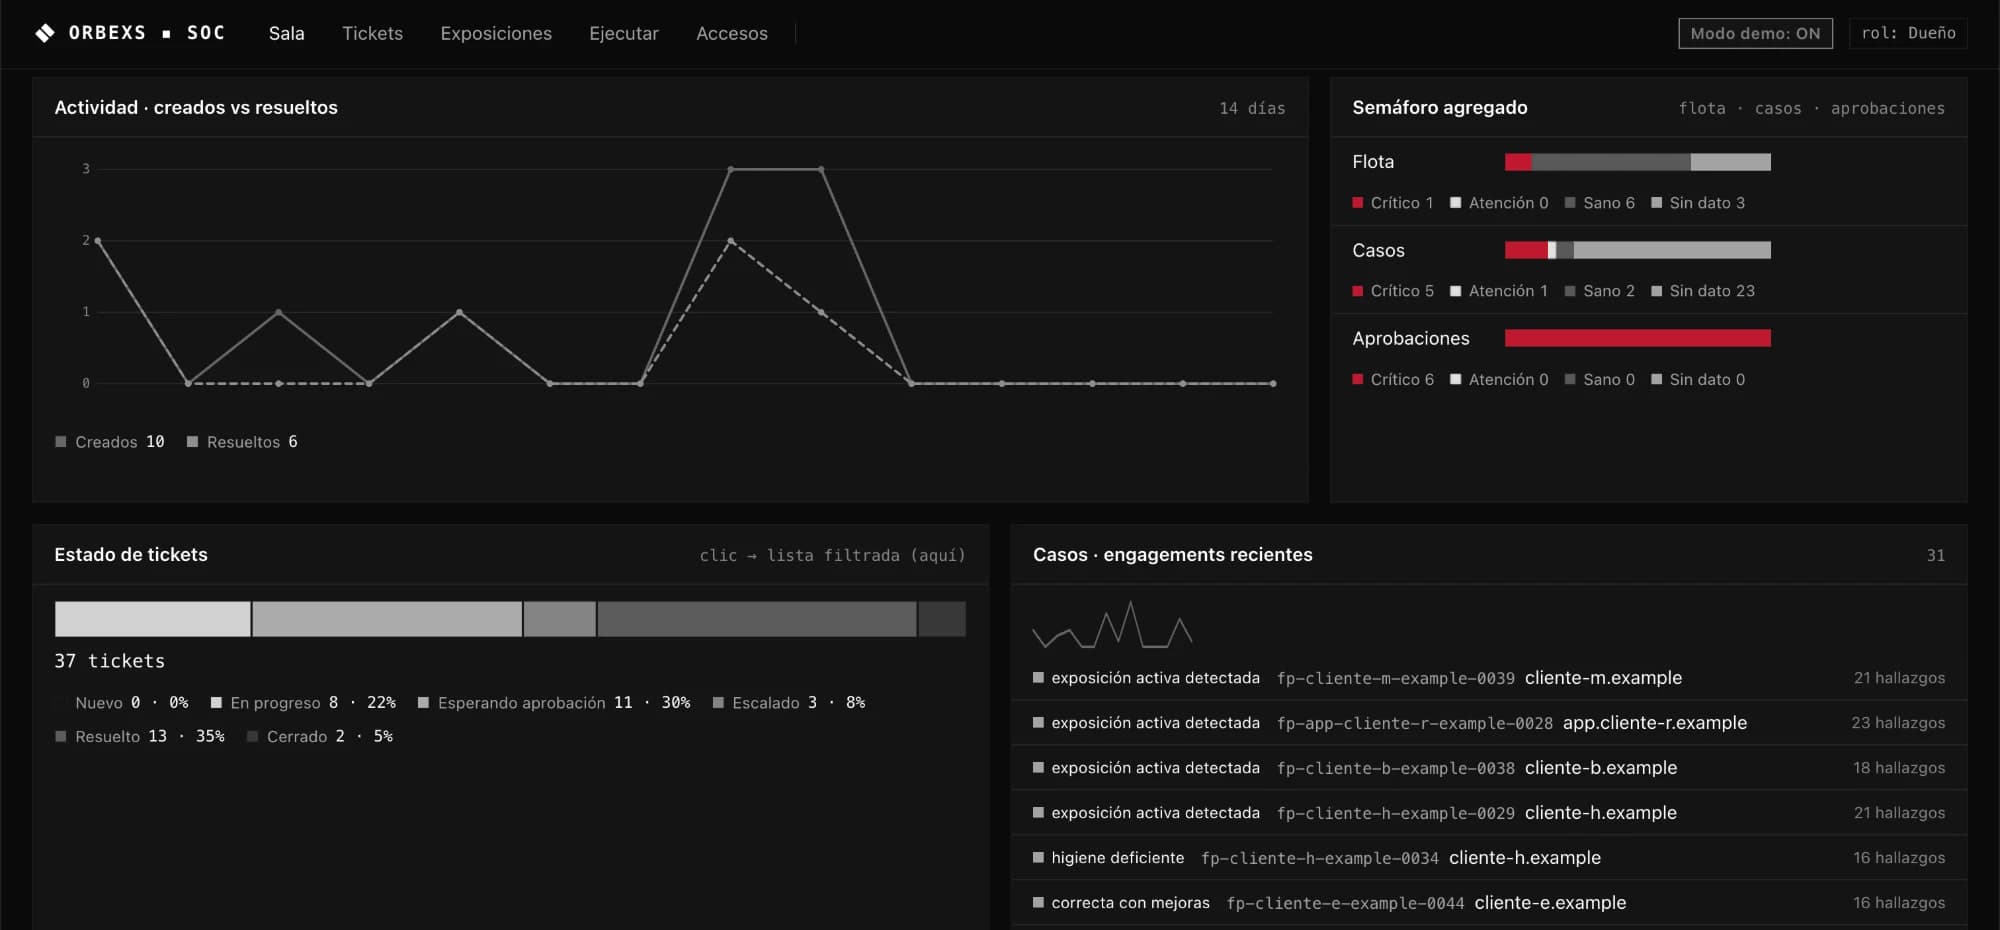
Nodo 1 (N1) console, full size
ONE SOFTWARE · THREE SCOPES
Three operational problems, one operator. N1 Security finds the risk; N1 Compliance turns it into hardening, verification and evidence. N1 Support keeps day-to-day operations moving.
/01
/02
/03
The scope is agreed with you. Actions with material production impact require human supervision and a maintenance window when appropriate.
N1 COMPLIANCE · CONTINUOUS OPERATIONS
N1 takes security reports, connects to authorized infrastructure, discovers configurations and relates findings to applicable controls. It proposes remediation, executes authorized changes, verifies them with a new scan and documents the result. Successive reviews help maintain that posture.
INTERACTIVE WALKTHROUGH · LOCAL DEMONSTRATION
Explore remediation that affects production. These buttons only change this example: they do not connect to infrastructure or execute real actions.
DETECTED
The scan identifies a TLS configuration that needs remediation.
PLAN GENERATED
N1 identifies the asset, proposes the change and assesses its impact.
WAITING FOR APPROVAL
The change may restart a service. N1 waits for approval and the agreed maintenance window.
APPROVED
In this example, an owner authorizes the plan for the agreed window. Execution remains bound to that scope.
REMEDIATING
N1 applies the change through the authorized interface and records the action and its result.
VERIFIED
N1 scans the asset again and compares the result with the initial finding.
EVIDENCE RECORDED
The follow-up report preserves the before and after states, authorization and verification.
The change may restart a service. N1 waits for approval and the agreed maintenance window.
N1 connects to environments such as AWS and Google Cloud Platform using the credentials and permissions the customer enables for the agreed scope.
It can act through APIs, CLI, SSH and tools in the authorized environment. Available mechanisms and changes depend on the asset, permissions and configuration.
A configuration change cannot close every gap. Policies, ownership, risk decisions and approvals require human involvement. Changes that depend on development or third parties are planned separately.
N1 EVIDENCE ENGINE
The follow-up report shows what was fixed, how it was done and what the new assessment confirmed. It also preserves what remains open. Your team can demonstrate the work to customers, internal stakeholders and auditors.
ILLUSTRATIVE COMPARISON · DEMONSTRATION DATA
Needs attention
Technical fix verified
These are readiness package components, depending on the applicable framework. N1 supplies reports and technical evidence; organizational documentation requires context, human review, approval and versioning. The complete package is prepared with your team and Orbexs, rather than generated automatically by a scan.
GOVERNANCE OF EVERY ACTION
N1 assesses impact before acting. Permission, risk and the operating window determine how each change executes. Reversibility alone does not make an action low risk.
LOW RISK
Tasks allowed by predefined policies can execute and be verified without individual approval.
MEDIUM RISK
Scope and authorization rules determine whether N1 can execute or must escalate before acting.
HIGH RISK · PRODUCTION
Critical changes, service restarts and other impactful actions are reviewed with a human and coordinated with the agreed window.
Every assessment runs under rules signed with you: assets, windows and limits. Anything outside the authorized scope is blocked.
Every action needs a valid permission. Without one, it doesn't run: the block happens before acting, not after.
Higher-impact actions ask for your approval. Denying is as easy as approving, and both decisions are logged.
Every step is recorded, and the report includes an integrity check that reveals any later alteration.
N1 SECURITY · AGENTIC CYBERSECURITY
An external diagnostic opens the conversation. Tests that interact with infrastructure and offensive validation are agreed separately, with explicit scope and authorization.
Starts with external fingerprinting: DNS, subdomains, DMARC, SPF and DKIM records where applicable, and public exposure signals. HTTPS and TLS checks are scoped according to how they interact with the asset.
Passive reconnaissance: public sources without testing defenses. Low-impact active checks require an authorized scope; they are not described as passive or as pentesting.
Assists and orchestrates authorized intrusive testing to demonstrate real vulnerabilities on agreed assets. Each finding is documented with severity, evidence and a recommendation.
ROE — Rules of Engagement: authorization, permitted assets, windows, actions, restrictions and traceability. Material impact requires human approval.
Autonomous agents and Orbexs specialists find what is truly exposed and test it with authorization, without extracting data. Every finding comes with its proof, its severity and a recommendation.
We don't stop at the report: we close the exposures alongside your team and strengthen configurations and controls, within the agreed scope and timeline.
We test the fixes again to confirm the exposure no longer reproduces within the assessed scope.
Every action and every finding is recorded with verifiable evidence, ready to show your posture to your leadership, your clients or an auditor.
Exposed credentials
Passwords and access keys published where they shouldn't be.
Misconfigured services
Whatever was left open or on factory settings.
Interfaces exposed to the internet without protection
Entry points to your systems that answer anyone.
Injection flaws in applications
Forms and applications that accept commands they should never run.
Encryption and security headers
Whether your sites protect what travels between the browser and your servers.
Email authentication
Whether anyone can send email pretending to be your organization.
Content management systems
Sites built with WordPress and similar tools, with their plugins.
Attack surface and subdomains
Everything your organization exposes to the internet, including what nobody remembers.
This is how every finding arrives: with its severity, proof that the risk is real and a record that no business data was accessed.
Access credential published on the client's public website.
Sealed evidence · valid chain
A TOUR OF THE CONSOLE
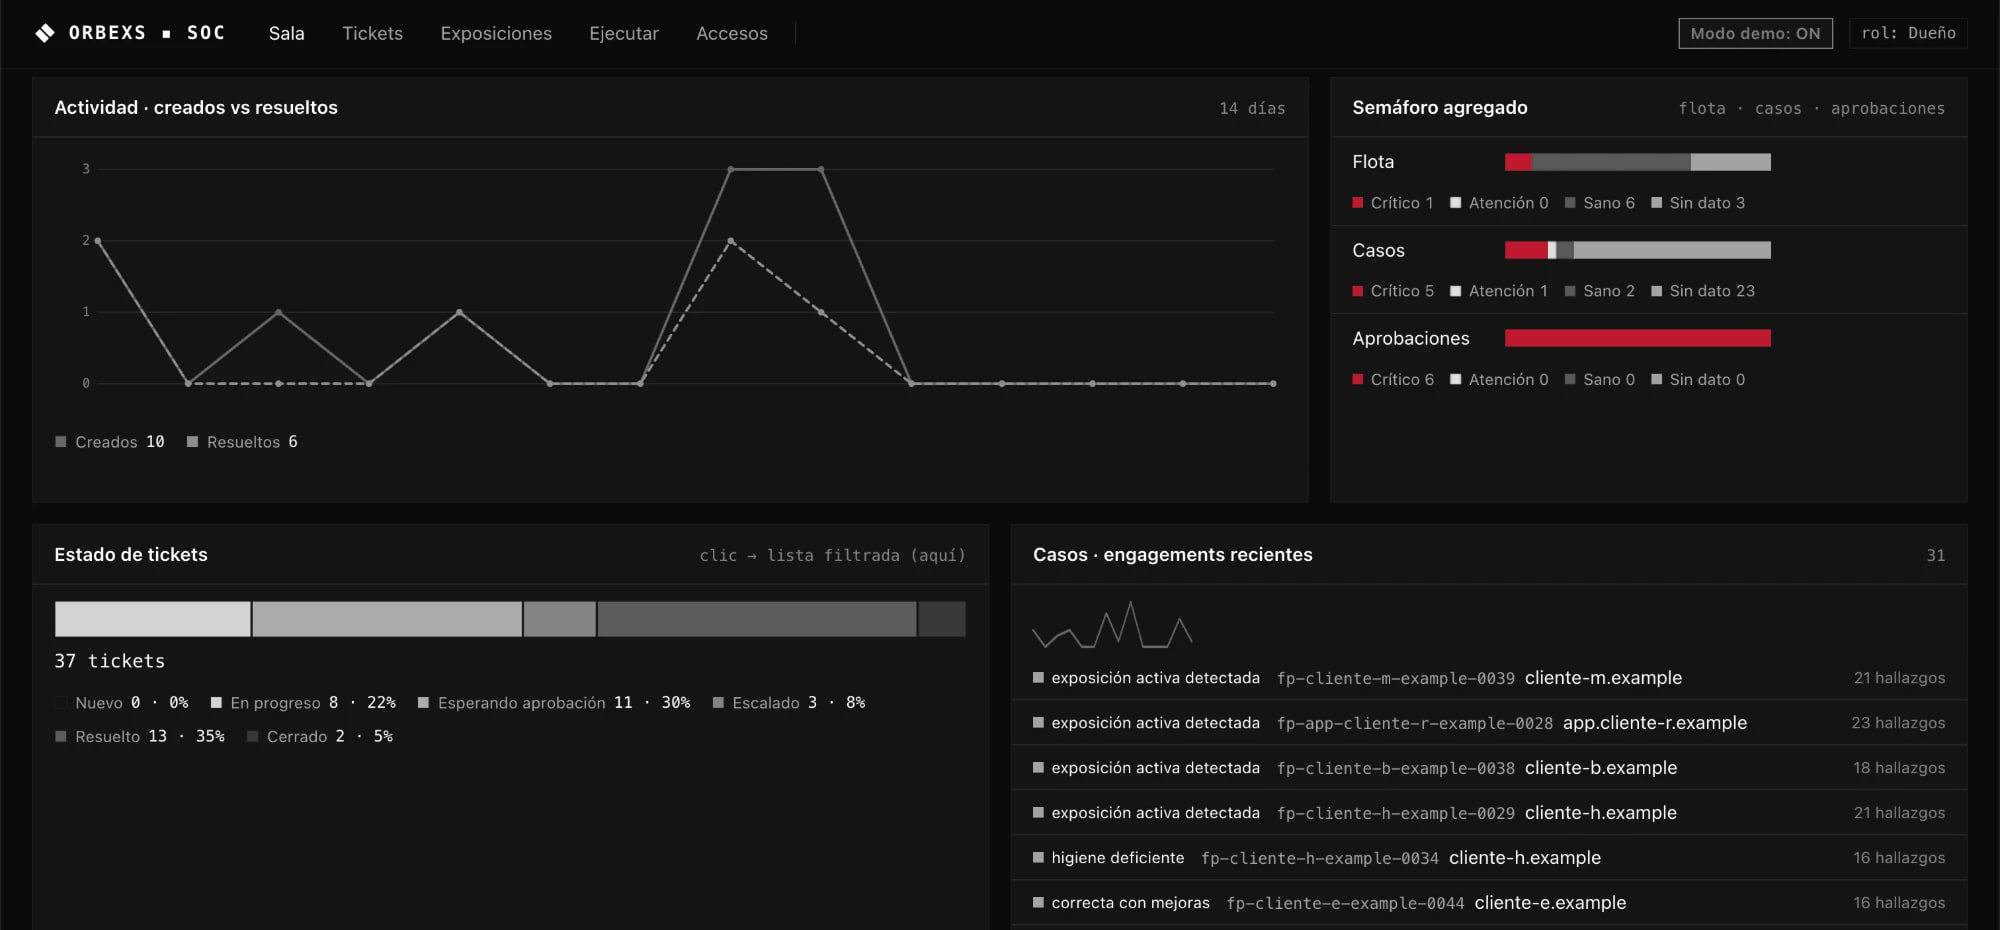
The main screen of the console brings together cases, the status of your devices and the assessments under way. Walk through it one area at a time.
Every case is followed until it is closed: created versus resolved, day by day.
The status of devices, cases and approvals, at a glance.
What is in progress, what awaits your approval and what is already closed.
Every assessment, with its status and its findings.
AGENTIC SUPPORT
Receives tickets, diagnoses issues and executes tasks on Windows, macOS and Linux within the authorized scope. It goes beyond suggesting steps: it applies permitted fixes, verifies the result and records the work. Critical changes escalate to a person.
In plain language, with no forms or codes.
Assesses risk and authorization rules before deciding how to act.
Permitted low-risk tasks execute and are verified. Reversibility does not replace authorization.
It asks for permission with context. Without your approval, it doesn't proceed.
Records state and verifies the result. Recovery or rollback is planned according to the task and what the environment supports.
It combines rules and artificial intelligence: if the artificial intelligence is unavailable, it keeps resolving with its rules.
It picks up open cases and resolves them at any hour, without anyone having to push them.
It connects to the devices in your operation and resolves on several at once, with a record for each one.
RESULTS IN REAL ENVIRONMENTS
What the assessments Orbexs has already run leave behind, with sealed evidence and within an authorized scope.
Aggregate figures from the assessments Orbexs has run in real environments.
From finding to closure: what we found, what we did and how it ended up.
Technology and health
Before
Publicly exposed services and assets, with configurations that widened the attack surface.
What Orbexs did
Reconnaissance, validation of each exposure and remediation alongside the client's technology team.
After
Findings fixed and a strengthened surface.
Legal sector
Before
Controls and configurations that needed strengthening.
What Orbexs did
Defensive and offensive assessment, plus strengthening of configurations and controls.
After
Controls reinforced and fixes verified in a second assessment.
Before
Technical findings with potential impact on the security of the environment.
What Orbexs did
Identification, technical remediation and a retest of the fixes.
After
Findings fixed, with evidence from the follow-up validation.
DISCOVER · REMEDIATE · OPERATE
Start by understanding your exposure, agree what to fix and maintain security operations with evidence. These are ways to work with the same N1, according to the scope you need.
External diagnostic and initial assessment. Active and intrusive tests are agreed under specific authorization.
What you receive
Hardening of authorized infrastructure, with impact assessment, supervision when needed and follow-up verification.
What you receive
Continuous security and compliance operations: successive reviews, authorized fixes and evidence to maintain and demonstrate your posture.
What you receive
ORBEXS · THE HUMAN LAYER
Orbexs supports security and compliance operations: prioritizing work, reviewing plans, coordinating production windows and interpreting evidence. Your team retains its decisions and approvals.
PLANS · ONGOING SECURITY AND SUPPORT
Start with a free diagnostic and choose how much support you need. Clear pricing, a report with concrete actions every month, and a person who reviews what N1 finds.
Companies of 20 to 150 people
USD 300/month
≈ COP 1.2 M per month
To know, every month, what an outsider sees of your company from the internet and what is worth closing first.
What it includes
For having it fixed, not just knowing
Recommended
USD 750/month
≈ COP 3.0 M per month
Everything in Vigía, plus time from our team to fix what the report points out.
What it includes
Banking, fintech and software selling to the US
From USD 1,500/month
≈ COP 6.0 M per month, from
For those who must answer for their security to customers, banks or auditors.
What it includes
Values in USD before taxes; COP equivalent for reference.
If you would rather fix what we found once, we quote by project. The price depends on size and on your infrastructure, on your own servers or in the cloud.
Project S
USD 600 – 1,200
A few fixes with a clear scope and simple infrastructure.
Project M
USD 1,500 – 3,500
Several areas to fix, or a mixed infrastructure.
Project L
USD 4,000 – 9,000
A broad infrastructure, with several sites or systems.
Every project ends with a before-and-after report and a new verification 30 days later.
EXPOSURE DIAGNOSTIC · NO COST
It is 100% passive: we look only at what is already public, without testing access or touching your systems. We do it only with the authorization of the domain owner.
We work aligned to a framework for the agreed scope. Certifications and reports (ISO 27001, SOC 2, the PCI scan) are issued by accredited, independent third parties; we help you prepare.
WHERE IT RUNS
Support, security and compliance work within a deployment and scope agreed with you.
ON YOUR INFRASTRUCTURE
The engine works from inside your network and the evidence stays within your perimeter. Any use of external services is defined with you in the scope.
IN THE CLOUD
A cell of its own for your organization: N1 shares no instance or data with other clients.
WHO IT IS FOR
Enterprise buyers request evidence of access, incident, risk and security controls. N1 helps turn operational work into a demonstrable posture.
A path from finding to authorized change, with verification and traceability, while retaining control of production.
Prioritized findings, coordinated remediation and evidence of what was fixed and what remains open.
A clear scope for hardening configurations and demonstrating the work to stakeholders.
Operational support for progressing toward independent assessment, alongside your organization’s professionals and owners.
What N1 does, what requires authorization and what belongs to an independent assessment.
Nodo 1 (N1) is one software with three scopes: Support for IT tasks, Security for assessments and reports, and Compliance for hardening, remediation and evidence. The contracted scope defines how each part participates.
It evaluates security reports, connects to authorized infrastructure using customer-enabled credentials and remediates configurations within scope. Complex changes or material impact require supervision and agreed windows. It then scans again and documents what was fixed, how and with what result.
No. Passive reconnaissance uses public information. Low-impact active checks are scoped and authorized according to their interaction with assets. Intrusive and offensive testing require specific authorization and ROE defining assets, windows, actions and restrictions.
Low-risk tasks can execute under predefined policies. Other tasks follow the scope’s authorization rules. For high risk or material production impact, N1 requires human approval and coordinates the maintenance window when appropriate.
No. N1 helps with hardening, technical control alignment and evidence to prepare for assessments such as ISO 27001 and ISO 42001; an independent certification body determines certification. SOC 2 Type II is an examination with a report issued by an independent auditor. Readiness also requires organizational processes, documentation and responsibilities. N1 does not guarantee certification or replace the auditor.
No. Orbexs can support technical and organizational measures related to GDPR. Remediation and reports contribute evidence; they do not independently establish complete compliance with legal data protection obligations.
Yes. It can support prioritization, review, documentation and coordination of windows and owners, as well as offer external assessments and audits with independent judgment. Certification and formal determinations belong to the authorized independent third party.
The control view on this page is conceptual and identified as the module’s evolution. Reports and technical evidence are part of current operations. Policies and the organizational package need your team’s input, human review, approval and version control; they are not presented as available automatic generation.
Only the authorization of the domain owner, which we verify before starting. The assessment is fully passive: we look at what is already public on the internet and run no tests against your systems.
Because the first month involves work that is not repeated: verifying your domains, building the baseline and, in Guardián and Cumplimiento, prioritizing remediation or analyzing gaps against the framework. In Vigía it is waived with an annual contract.
Guardián and Cumplimiento hours do not roll over from one month to the next. If you need more in a given month, we quote them separately before doing anything.
Before starting, we agree in writing on the scope and the success criteria. If at the end of the pilot you do not see value, we refund what you paid; if you continue, that amount is credited to your contract.
No. Prices are in US dollars and before taxes; the Colombian peso equivalent is for reference and may vary with the exchange rate.
Schedule a technical session to see N1 in action and define an external diagnostic within an agreed scope. Then decide what to fix and how to maintain it.
See N1 in action